- Origin
- Unknown
- Motivation
- Financial
- First seen
- Aug 9, 2023
- Last activity
- 15 hours ago
- Techniques
- 25
- Victims posted
- 1,020
About
INC Ransom is a ransomware and data extortion threat group associated with the deployment of INC Ransomware that has been active since at least July 2023. INC Ransom has targeted organizations worldwide most commonly in the industrial, healthcare, and education sectors in the US and Europe.
Victims per month (12 months)
35
12
44
01
41
02
56
03
40
04
32
05
31
06
38
07
43
08
35
09
27
10
53
11
Leak site as captured
17 Nov 2026 14:43 UTC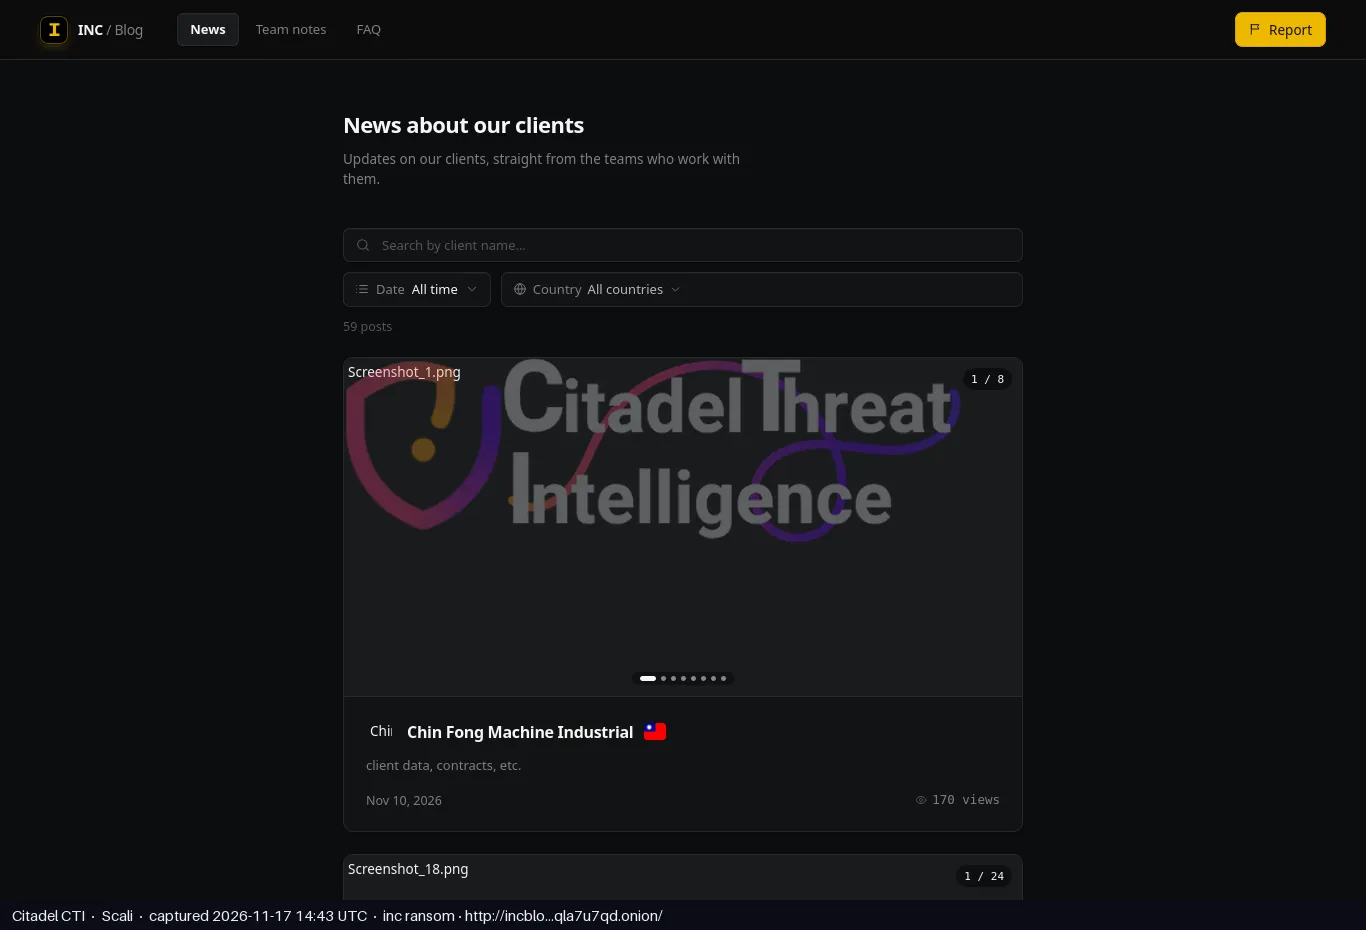
Leak sites & mirrors
4 online 8 offline
incbac…rwdcityd.onion
leak site
incblo…qla7u7qd.onion
leak site
incpay…ssx6qkid.onion
chat
incs3e…njiowqqd.onion
file server
in…t.blog
leak site
in…t.su
leak site
in…d.top
leak site
incbac…giemr7qd.onion
leak site
incbac…mtukn4yd.onion
leak site
incblo…sajldoad.onion
leak site
incblo…dyyzzxid.onion
leak site
incpay…342bdnad.onion
chat
Addresses collected and maintained by Amit Cohen Scali, CTI Research Lead at Citadel
Tools & malware
7-Zip
AdFind
Advanced IP Scanner
AnyDesk
BackBlaze
Bitvise SSH Client
esentutl
Finger
INC Ransomware
MEGA
Mimikatz
Net
Nltest
PsExec
RClone
Rclone
Restic
s5cmd
SoftPerfect NetScan
Tor
WinRAR
Malware · tools (often legitimate software abused)
Contacts & addresses
How the group asks to be reached and where it publishes, as open sources list them. Full addresses: approved researchers only.
- Sites · 1
-
in…g.su new - Deep · deepdarkCTI
Attribution reflects public research and can change. Technique data: MITRE ATT&CK® (see notices).